


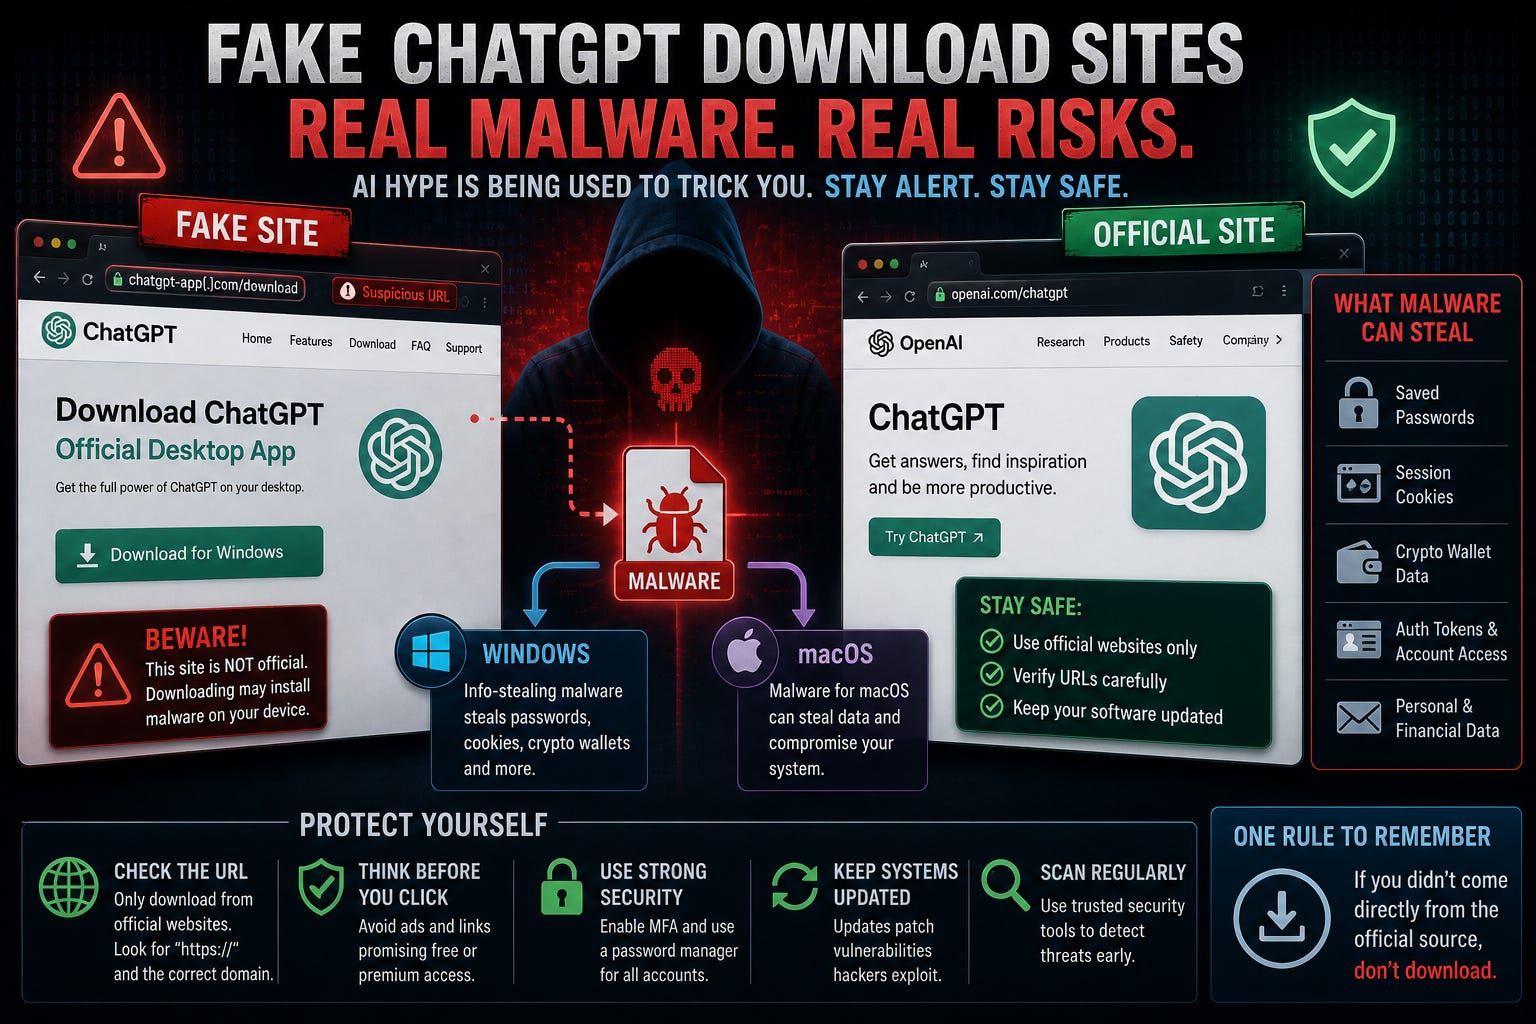
Artificial intelligence has become one of the most searched technology topics in the world. Millions of users search for ChatGPT every day, making it an attractive target for cybercriminals looking to distribute malware.
According to recent research from Malwarebytes, threat actors are creating convincing fake ChatGPT download websites that trick users into installing malicious software on both Windows and macOS systems.[1]
While the sites appear legitimate at first glance, the downloaded files contain malware capable of stealing credentials, collecting sensitive information, and compromising devices.
The campaign demonstrates an increasingly common trend in cybersecurity:
Attackers no longer need sophisticated exploits when social engineering works just as well.
By exploiting the popularity of AI tools, cybercriminals are finding new ways to convince users to lower their guard and install malicious software voluntarily.
For everyday users, this serves as a reminder that not every website claiming to offer AI tools can be trusted.
Why It’s Important
The rise of fake software websites is not new.
What makes this campaign different is the use of trusted AI brands like ChatGPT as bait.
Cybercriminals understand that many users are searching for:
ChatGPT desktop applications.
AI productivity tools.
Free premium AI access.
New AI features.
Alternative AI platforms.
When users encounter a convincing website promising these capabilities, they may be more likely to download software without carefully verifying the source.
According to Malwarebytes researchers, the fake sites distribute malware families capable of stealing browser credentials, cryptocurrency wallets, session cookies, and other sensitive information.[1]
That creates risks extending far beyond a single infected device.
A stolen browser session can allow attackers to bypass passwords entirely.
Think of it like someone stealing your house keys while you are still inside the home.
They do not need to break the lock if they already possess the credentials needed to walk through the front door.
Security researchers have repeatedly observed similar tactics involving fake versions of:
Zoom.
Microsoft Teams.
Google Chrome.
Telegram.
Cryptocurrency wallets.[2]
Now AI platforms have joined the list of brands actively abused by cybercriminals.
What It Is / How It Works
According to Malwarebytes, the attackers created websites closely resembling legitimate ChatGPT download pages.[1]
The sites use familiar branding, logos, and marketing language designed to convince visitors they are downloading an official application.
Once a victim downloads and executes the file, the malware begins installing additional components in the background.
Researchers observed different payloads depending on the victim’s operating system.
Windows Infections
For Windows users, the campaign reportedly delivered information stealing malware designed to collect:
Browser credentials.
Stored passwords.
Cryptocurrency wallet data.
Authentication tokens.
Session cookies.[1]
These malware families often target browsers because they contain a wealth of sensitive information.
Rather than stealing passwords directly, attackers increasingly focus on session cookies, which can sometimes provide access to accounts without requiring a password or multi-factor authentication code.[4]
macOS Infections
Mac users were not spared.
Malwarebytes researchers identified macOS specific malware variants disguised as AI software installers.[1]
This reflects a larger trend that many security researchers have observed over the past several years.
While Windows remains the primary target, macOS malware continues growing as attackers recognize the increasing popularity of Apple devices.[5]
Search Engine Manipulation
Many fake software campaigns rely on search engine optimization and malicious advertising.
Researchers have documented cases where attackers purchase advertisements that appear above legitimate search results.[6]
Users searching for terms like:
“Download ChatGPT”
or
“ChatGPT desktop app”
may encounter malicious websites before reaching official sources.
That visibility gives attackers an enormous advantage.
The Bigger Problem: AI Brand Abuse Is Accelerating
The fake ChatGPT campaign is part of a much larger trend involving AI related scams and malware.
Since ChatGPT’s launch, security researchers have documented:
Fake ChatGPT browser extensions.
Counterfeit AI mobile applications.
Phishing pages impersonating OpenAI.
Fraudulent AI investment schemes.
Malware distributed through AI-themed websites.[7][8]
Cybercriminals are exploiting the public’s excitement around AI in much the same way they previously exploited cryptocurrency, remote work tools, and social media platforms.
The underlying strategy remains the same:
Take something people already trust and use it as a delivery mechanism.
Researchers at Check Point and Cisco Talos have both reported increased AI themed phishing campaigns targeting businesses and consumers alike.[8][9]
As AI adoption grows, these attacks will likely become even more common.
Unfortunately, many victims assume they are interacting with legitimate software because the branding appears authentic.
Visual familiarity has become one of the most powerful social engineering tools available.
How to Mitigate
Protecting yourself from fake software websites requires a combination of caution and good security habits.
Download Software Only From Official Sources
The safest approach is visiting a vendor’s official website directly.
Avoid relying exclusively on search results or advertisements.
For ChatGPT, users should download software only from OpenAI’s official channels.
Verify URLs Carefully
Attackers frequently register lookalike domains that differ by only one or two characters.
Examples may include:
Misspelled words.
Extra hyphens.
Alternate top level domains.
Additional words such as “download” or “free.”
Always verify the full URL before downloading anything.
Enable Multi-Factor Authentication
Even if credentials are stolen, MFA can provide an additional layer of protection.
Enable MFA on:
Email accounts.
Financial services.
Cloud storage.
Social media accounts.
Use Endpoint Protection
One practical security tool worth considering is Malwarebytes Premium.
Behavior based detection can often identify suspicious activity even when malware bypasses traditional signature based defenses.
Want to support my work? Consider buying me a coffee ☕
How to Configure/Use Protective Measures
Preventing malware infections is easier than recovering from one.
Here are several practical steps users can implement immediately.
Use a Password Manager
Password managers generate unique credentials for every account.
This reduces the damage if one account becomes compromised.
Keep Browsers Updated
Modern browsers include security protections against:
Malicious downloads.
Phishing websites.
Dangerous scripts.
Running outdated software increases risk significantly.
Review Browser Extensions
Many malware campaigns use fake browser add-ons.
Audit installed extensions regularly and remove anything unnecessary.
Monitor Account Activity
Watch for:
Unexpected login alerts.
Password reset notifications.
New device registrations.
Suspicious financial transactions.
Early detection can dramatically reduce damage after credential theft.
Train Yourself to Pause Before Downloading
The most effective security control remains human judgment.
If a website promises free premium access, exclusive AI features, or unusually attractive offers, verify the source before clicking.
A few seconds of caution can prevent weeks of recovery.
Full Disclosure: Malwarebytes is an affiliate partner, which means I may earn a commission if you purchase through links in this article. However, Malwarebytes did not sponsor this article, review its contents, or influence my analysis in any way. All opinions expressed are my own.
Feature Highlight: Proactive Defense Against Infostealers
Traditional antivirus relies on static signatures, but modern infostealers like the Odyssey variant targeting Mac users mutate constantly to evade detection. Malwarebytes Premium uses advanced, behavior based detection to stop malware the moment it tries to execute, shielding your browser data, session cookies, and crypto wallets even if you accidentally click a malicious link.
Real-Time Web Protection: Blocks access to known lookalike domains and malicious advertising campaigns before they can drop payloads.
MalwarebytesDual-Platform Coverage: Enterprise grade security tailored specifically for both Windows and macOS vulnerabilities.
Malwarebytes
👉 Protect Your Devices with Malwarebytes Premium
Closing encouragement
The fake ChatGPT malware campaign highlights a lesson cybersecurity professionals have repeated for years:
Attackers follow attention.
Where users go, cybercriminals eventually follow.
As AI tools become more popular, we should expect scammers and malware operators to increasingly exploit trusted brands, familiar logos, and growing public curiosity.
The good news is that most of these attacks remain preventable.
Verifying download sources, using strong authentication, keeping systems updated, and maintaining healthy skepticism can stop many threats before they begin.
Technology will continue evolving rapidly.
Developing safe habits is what helps users stay protected no matter what new platform comes next.
Have you ever encountered a fake software download page that looked legitimate at first glance?
Sources
[1] Malwarebytes, “Fake ChatGPT Download Site Infects Windows and Mac Users With Malware” https://www.malwarebytes.com/blog/threat-intel/2026/05/fake-chatgpt-download-site-infects-windows-and-mac-users-with-malware
[2] Microsoft Security Blog, “Disrupting Threats Targeting Microsoft Teams” https://www.microsoft.com/en-us/security/blog/2025/10/07/disrupting-threats-targeting-microsoft-teams/
[4] CISA, “Strengthening Security Configurations to Defend Against Attackers Targeting Cloud Services” https://www.cisa.gov/news-events/analysis-reports/ar21-013a
[5] Malwarebytes, “Macs Targeted by Infostealers in New Era of Cyberthreats” https://www.malwarebytes.com/blog/mobile/2025/02/macs-targeted-by-info-stealers-in-new-era-of-cyberthreats
[6] FBI Internet Crime Complaint Center (IC3), “Cyber Criminals Impersonating Brands Using Search Engine Advertisement Services to Defraud Users” https://www.ic3.gov/PSA/2022/PSA221221
[7] Check Point Research, “OPWNAI: Cybercriminals Starting to Use ChatGPT” https://research.checkpoint.com/2023/opwnai-cybercriminals-starting-to-use-chatgpt/
[8] Cisco Talos, “Year in Review: AI-Based Threats” https://blog.talosintelligence.com/year-in-review-ai-based-threats/
[9] Check Point Research, “The State of AI in Cyber Security” https://research.checkpoint.com/2025/sate-of-ai-in-cyber-security/
[10] Cisco Talos, “2025 Year in Review” https://blog.talosintelligence.com/2025yearinreview/