


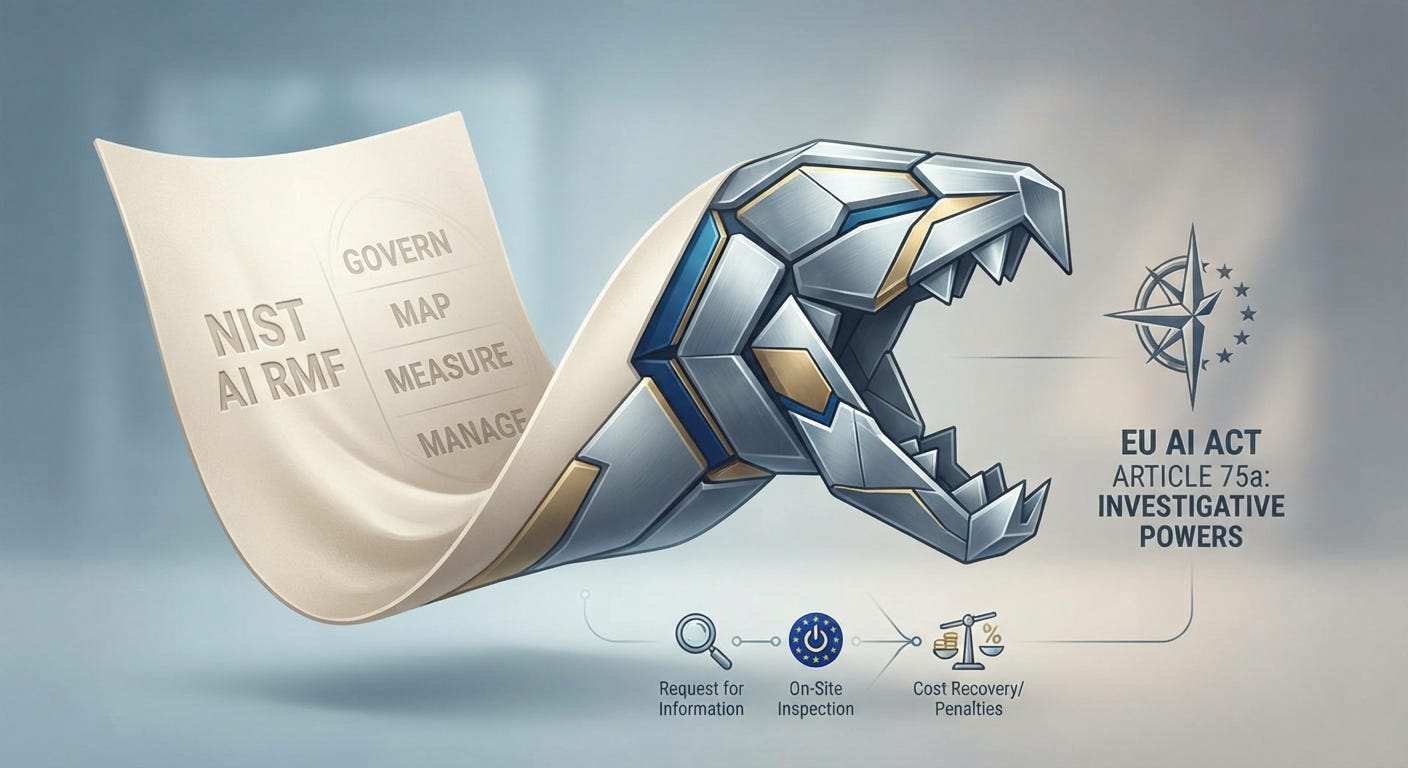
For the past two years, AI governance professionals have operated in a comfortable ambiguity. We built risk management programs aligned to the NIST AI Risk Management Framework, mapped controls, documented processes, and assured our boards that we were “doing AI governance properly.” The NIST framework, published in January 2023, became the de facto lingua franca for responsible AI voluntary, principled, and increasingly used by government agencies and enterprises as a practical foundation for AI risk management.
But there was always a nagging question lurking beneath the surface. The question was never whether NIST could enforce compliance. It was what would happen when organizations had to translate voluntary risk management practices into legally enforceable obligations. What happens when a regulator with actual enforcement power comes knocking?
That moment arrived on 2 August 2026.
The NIST Enforcement Gap
Let’s be clear about what the NIST AI RMF was designed to do and what it wasn’t. The framework organises AI risk management into four functions: Govern, Map, Measure, and Manage. It provides an invaluable operational structure for identifying risks, establishing accountability, and implementing controls. For organisations serious about AI governance, it remains one of the most useful operational frameworks for building a coherent AI risk management program.
What NIST never provided was enforcement. No fines. No dawn raids. No regulatory body with the power to compel access to your models or impose penalties calculated as a percentage of global turnover. The framework was, by design, a voluntary guide, a roadmap without a traffic cop.
This created what I call the “enforcement gap”: organisations could claim alignment with NIST principles while falling short on actual compliance, knowing that the consequences were reputational rather than financial. The gap between “we follow the framework” and “we are legally compliant” remained comfortably wide.
The EU AI Act has now slammed that gap shut.
The AI Office Gets Teeth
Under the EU AI Act’s enforcement framework, responsibility is divided between the European Commission’s AI Office, national competent authorities, and the European Data Protection Supervisor. The AI Office has exclusive competence over specified AI systems based on general purpose AI models and over AI systems that constitute or are integrated into very large online platforms or very large online search engines, subject to the exceptions and scope limitations in Article 75.
For high-risk AI systems outside the AI Office’s Article 75 competence, supervision and enforcement generally remain with the relevant national competent authorities.
But it’s the nature of those powers that should command attention.
Under the newly strengthened Article 75a, the AI Office has acquired a market surveillance enforcement toolkit with powers that go well beyond a conventional compliance questionnaire. Its officials may enter any business premises, land, or property in the Union. They can examine books, data, and other records regardless of format. They can take copies or extracts. They can require oral explanations on the spot and record the responses. They can even seal premises, books, or records for the duration of an inspection.
Let that sink in. This is not a documentation review conducted by correspondence. This is the toolkit of a regulator that expects to find things.
It’s worth noting that this heavy enforcement toolkit applies specifically to operators under the AI Office’s direct competence GPAI integrated systems and VLOPs. Standard enterprises deploying high-risk AI systems interact primarily with national competent authorities, who operate under different procedural frameworks and penalty structures.
The Cost Recovery Power
Perhaps the most consequential and least discussed new power is the AI Office’s ability to recover costs. Article 75a allows the AI Office to fully recover the costs of its supervision and enforcement activities in cases involving non-compliance, including human and technical resources.
This is a subtle but profound shift. In traditional regulatory models, enforcement costs are borne by the taxpayer. The regulator investigates, the public pays, and the fined company simply treats the penalty as a cost of doing business. Cost recovery changes the calculus entirely. The potential financial exposure therefore extends beyond the eventual administrative fine. An organisation found to be non-compliant may face both the regulatory penalty and the recoverable costs associated with the enforcement activity.
For organisations weighing the cost of proactive compliance against the risk of enforcement, this tilts the equation decisively. The question is no longer “What’s the fine if we’re caught?” but “What’s the cost of the investigation that finds us?”
Penalties That Bite
The penalty structure under the AI Act is tiered and substantial. For prohibited AI practices social scoring, exploitative manipulation, and specific banned biometric practices fines can reach €35 million or 7% of total worldwide annual turnover, whichever is higher. Other violations, including breaches of GPAI obligations and high-risk requirements, can result in fines up to €15 million or 3% of worldwide turnover.
Critically, for operators under AI Office supervision, the fining base is wider than for those under national supervision. Under Article 75c(4)(a), the AI Office may fine an operator up to the Article 99(4) tier for infringing any applicable provision of the Regulation including provisions that Article 99(4) does not explicitly list. For operators under national supervision, that list is exhaustive. For those under AI Office supervision, it is not.
This is the detail that separates informed analysis from generic commentary. The AI Office isn’t just enforcing the same rules with more resources it’s enforcing a broader set of obligations with greater penalty exposure.
The AI Office can also impose periodic penalty payments of up to 5% of average daily income or worldwide annual turnover, as specified by the Regulation, for each day of non-compliance. These are designed to compel cooperation to force operators to submit to investigations, respond to information requests, and comply with corrective measures. The meter runs daily.
And here’s the detail that should keep compliance officers awake: the AI Office’s enforcement powers are subject to a five year limitation period, beginning when the infringement is committed, or, for continuing or repeated infringements, when the infringement ceases. The Commission must publish decisions adopted under Articles 75b and 75c, including the names of the parties and the main content of the decision, subject to protections for confidential information. This is not a regime designed to be quietly navigated.
An Inspection Is an Operational Event
An inspection is not just a legal event it’s an operational one. Organisations within the AI Office’s competence should have an inspection response procedure before they need one. Employees should know who is authorised to interact with inspectors. Legal and compliance teams should understand escalation procedures. Critical AI documentation should be organised so that it can be retrieved quickly.
Article 75a incorporates powers under Regulation (EU) 2019/1020, the market surveillance regulation. Where national law requires judicial authorisation for inspections, the AI Office must seek that authorisation, and the national court must verify that the proposed coercive measures are neither arbitrary nor excessive. This is a genuine procedural safeguard but it’s not a shield against well prepared regulators.
The practical reality is that the companies that get hurt are those that cannot produce a technical file, a conformity assessment, or logs when asked. The investigation itself becomes a significant compliance event, even before any fine is imposed.
Why NIST Alignment Is Your Best Defence
Here’s where the story becomes constructive rather than merely cautionary.
The EU AI Act and NIST AI RMF are not competing frameworks. They are complementary and organisations that have invested in NIST alignment are better positioned for EU compliance than they might realise. Crosswalk analyses mapping EU AI Act obligations to NIST AI RMF controls reveal substantial overlap. The Govern function maps to AI Act requirements around accountability and risk management. The Map function aligns with obligations to identify and document risks. Measure and Manage correspond to testing, monitoring, and corrective action requirements.
However, and this is crucial, the mapping is not one-to-one. Crosswalk analyses identify several EU AI Act obligations that have no direct equivalent in NIST AI RMF, including conformity assessment, CE marking, EU database registration, and, where applicable, appointment of an EU authorised representative for certain providers located outside the Union.
The strategic implication is clear: NIST alignment provides a strong foundation, but it must be supplemented with EU specific compliance work. Organisations that treat their NIST program as sufficient will find themselves exposed. Organisations that use NIST as the operational backbone for a broader EU compliance strategy will be far better positioned when the AI Office comes calling.
The Investigative Reality
What does an AI Office investigation actually look like? The process typically begins with a request for information. Simple RFIs carry fines only if responses are incorrect or misleading voluntary, but with consequences for inaccuracy. Formal RFIs issued by Commission decision carry fines for failure to respond or incomplete responses.
For GPAI models, the AI Office can conduct evaluations directly or through appointed independent experts, requiring providers to grant access to their models. It can request providers to take measures, including restricting public availability of a model if necessary.
For AI systems under its supervision, the Office can conduct interviews and inspections. Before requesting corrective measures, it may initiate a structured dialogue with the operator, during which the operator can propose commitments that the AI Office may make binding. This “commitment” mechanism offers a path to resolution without formal penalty but only for organisations that can demonstrate genuine compliance capability.
Your Action Plan
The enforcement gap has closed. Here’s how to prepare:
1. Map your NIST controls to EU AI Act obligations. Use available crosswalk tools to identify which of your existing NIST AI RMF controls satisfy EU requirements and which have no equivalent. The genuine gaps (conformity assessment, CE marking, EU database registration, and authorised representation requirements) require dedicated EU specific work.
2. Perform an EU gap analysis for technical documentation. Article 11 and Annex IV require specific documentation formats that NIST does not prescribe. If you’ve completed NIST Map activities, you have the content but you must format it for EU compliance. Build your technical file now, before an investigation forces the issue.
3. Establish an audit ready logging protocol. Ensure that required logs and records are automatically generated, retained for the applicable period, and readily retrievable. Article 12 establishes specific record keeping requirements for high-risk AI systems, while Article 72 requires providers of high-risk AI systems to establish and document post market monitoring, and Article 73 establishes serious incident reporting obligations. If you cannot produce required documentation within the specified timeframe, you face fines for incomplete responses.
The EU AI Act’s enforcement powers represent a fundamental shift in the AI governance landscape. For the first time, organisations face a regulator with the tools, the mandate, and the financial mechanism to conduct thorough investigations and impose meaningful penalties.
NIST alignment remains essential, it provides the operational structure that makes compliance achievable. But NIST alignment alone is no longer sufficient. The enforcement gap has closed, and the organisations that recognise this will be the ones that thrive in the new regulatory reality.
The question is no longer whether you have an AI governance program. It’s whether that program can withstand an investigation.
What’s your organisation’s biggest concern about EU AI Act enforcement the investigative powers, the cost recovery mechanism, or the challenge of mapping NIST controls to EU obligations? Share your perspective in the comments.