


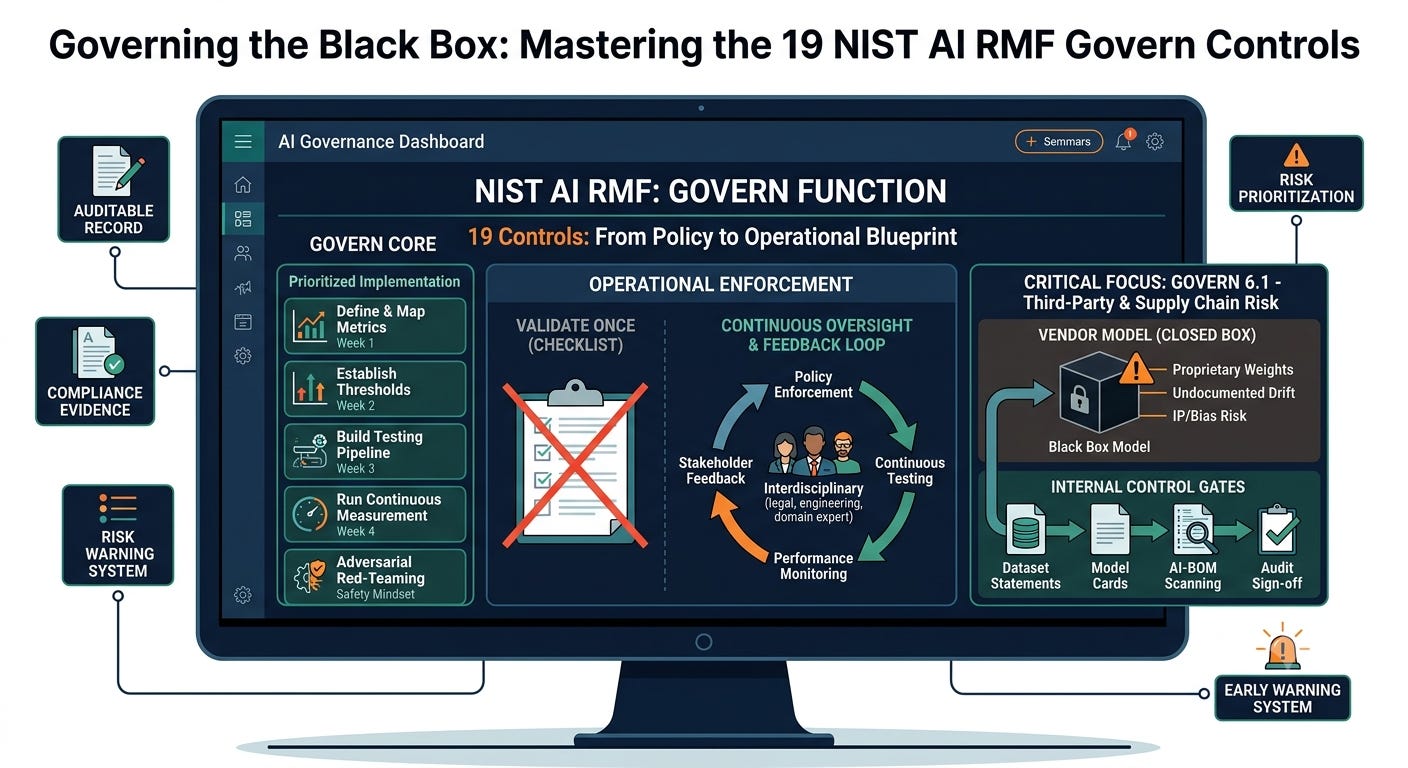
The integration of artificial intelligence into enterprise operations introduces structural risks that traditional enterprise risk management frameworks struggle to address. Unlike static software systems, machine learning models display non-deterministic behaviors, algorithmic drift, and complex socio-technical dependencies. To manage these risks, NIST released the AI Risk Management Framework (AI RMF 1.0) along with its accompanying AI RMF Playbook.
At the center of the framework sits the Govern function. Governance is not a transient compliance check. It is the foundational infrastructure that informs the Map, Measure, and Manage functions across the AI system lifecycle. Governed systems require clear lines of communication, documented risk tolerances, continuous oversight, and comprehensive accountability structures.
Across the 19 subcategories of the Govern function, organizations embed a safety-first, risk-aware culture directly into their technology stack.
Breakdown of the 19 NIST AI RMF Govern Controls
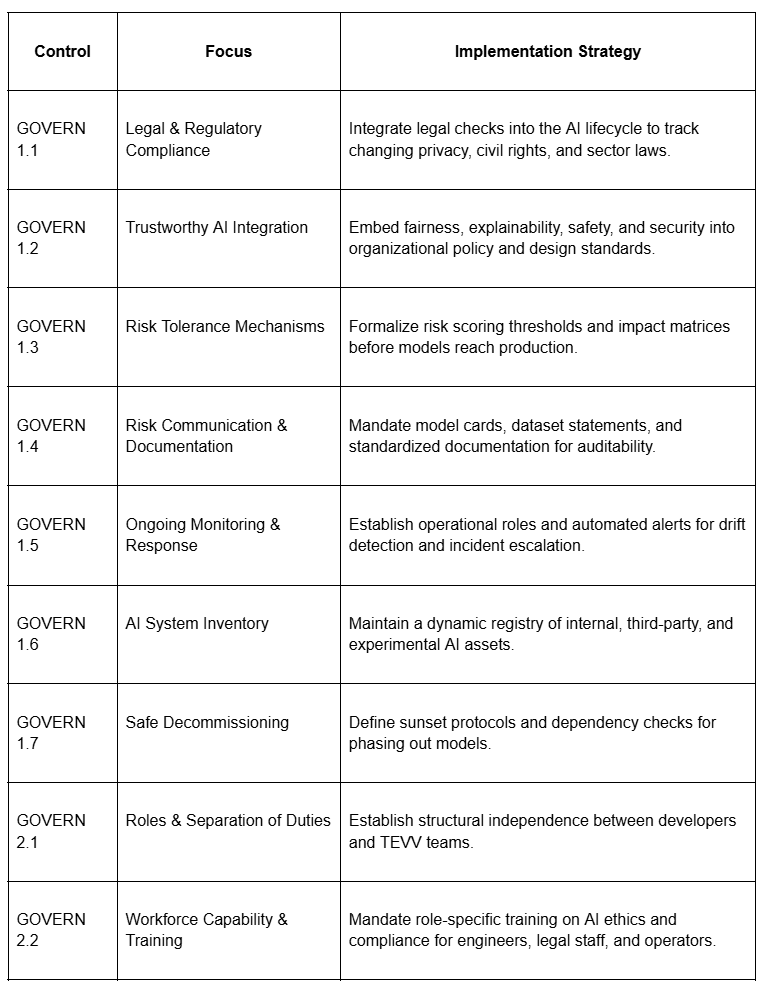
The Govern function splits into six categories containing 19 subcategories total.
GOVERN 1: Policies, Processes, Procedures, and Practices
1.1 Legal & Regulatory Requirements continually monitor, map, and document applicable legal, regulatory, and privacy requirements (non-discrimination laws, civil rights acts, data protection rules).
1.2 Trustworthy AI Integration embed safety, security, explainability, and fairness directly into organizational policy.
1.3 Risk Tolerance Mechanisms establish formal risk scales to define acceptable thresholds based on likelihood and impact.
1.4 Risk Management Transparency enforce standardized documentation, including model cards, dataset statements, and line-of-sight tracking for all AI deployments.
1.5 Ongoing Monitoring & Periodic Review define operational roles and schedules for real-time tracking and incident response.
1.6 AI System Inventory maintain an enterprise-wide inventory of internal, external, and experimental AI artifacts, code repositories, and owners.
1.7 Decommissioning Protocols define procedures to phase out models safely without cascading failures or compliance violations.
GOVERN 2: Accountability Structures and Workforce Readiness
2.1 Defined Roles and Responsibilities separate development teams from independent test and evaluation (TEVV) teams to eliminate groupthink and confirmation bias.
2.2 Workforce Training & Awareness train technical developers, legal teams, and executive operators on socio-technical risks and regulatory compliance.
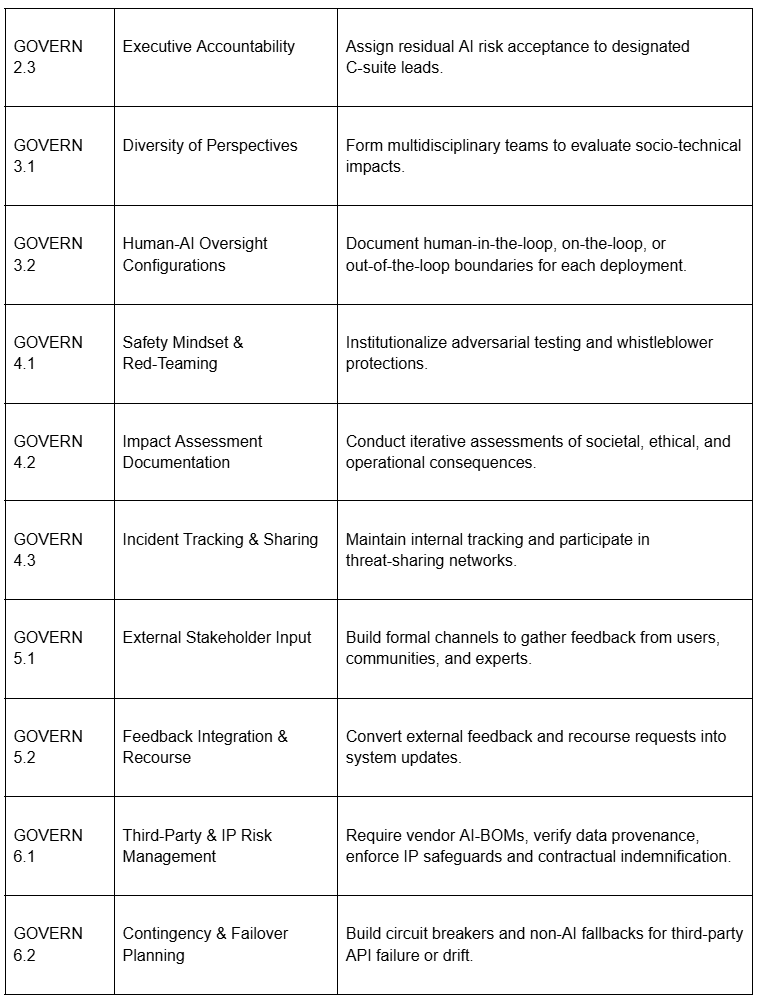
2.3 Executive Leadership Responsibility assign explicit accountability for AI risks, model approvals, and residual risk acceptance to executive leadership.
GOVERN 3: Diversity of Perspectives and Human Oversight
3.1 Diversity of Perspectives mandate interdisciplinary teams (technical experts, social scientists, legal personnel, domain specialists) throughout design and risk mapping.
3.2 Human-AI Oversight Configurations establish clear boundaries for human-in-the-loop, human-on-the-loop, and human-out-of-the-loop systems.
GOVERN 4: Organizational Culture and Impact Assessment
4.1 Safety-First Mindset & Red-Teaming foster independent model audits, adversarial red-teaming, and whistleblower protections.
4.2 Impact Assessment Documentation require iterative algorithmic impact assessments before and during deployment.
4.3 Testing, Incident Tracking, and Information Sharing build pipelines for reporting model errors, tracking near-misses, and contributing to threat databases like the AI Incident Database.
GOVERN 5: Stakeholder Engagement and Feedback Loops
5.1 External Stakeholder Input establish feedback mechanisms to collect insights from external users, affected communities, and domain experts.
5.2 Integration of Adjudicated Feedback build formal loops to translate community feedback, bug bounties, and recourse requests into system changes.
GOVERN 6: Third-Party and Supply Chain Risk Management
6.1 Vendor & IP Risk Management extend governance to vendor-supplied models, third-party APIs, pre-trained datasets, and open-source foundations.
6.2 Contingency & Failover Planning establish automated or procedural fallbacks and decommissioning triggers when third-party systems fail.
The audit nightmare: the hardest control to implement
Defining roles under GOVERN 2.1 or building an inventory under GOVERN 1.6 takes organizational discipline. GOVERN 6.1, third-party risk and intellectual property, consistently causes the most failures in independent compliance audits.
Why it breaks down:
The vendor black box. Enterprises rely on proprietary APIs, fine-tuned foundational models, and commercial SaaS platforms. Vendors routinely refuse to disclose training data composition, system architecture, or evaluation metrics, citing trade secrets. Risk officers can’t verify data provenance, non-infringement, or underlying bias.
Upstream data contamination. Under GOVERN 6.1, organizations stay legally liable for IP infringement, copyrighted training data, or privacy violations embedded in third-party models. Proving a vendor’s pretrained model contains no protected data, without visibility into its training set, is close to impossible.
Shadow AI procurement. Software teams integrate commercial APIs or open-source weights into pipelines quickly. Without automated AI-specific software bill of materials (AI-BOM) scanning, unvetted third-party software bypasses risk controls entirely.
Architectural blueprint for compliance execution
Governance as a technical enabler
Working through the 19 subcategories of the Govern function means moving away from static policy binders toward integrated, code-level enforcement. Governance doesn’t slow engineering velocity. It provides the operational guardrails needed to scale AI safely across the enterprise.
Organizations that address third-party vendor management (GOVERN 6.1), independent testing separation (GOVERN 2.1), and automated system inventorying (GOVERN 1.6) early build systems that pass audits and protect organizational trust.
Join the conversation: When evaluating third-party AI models or vendor APIs in your environment, how do you balance the speed of adopting powerful external models against the audit risks of closed source, black-box training data? Leave a comment below.