


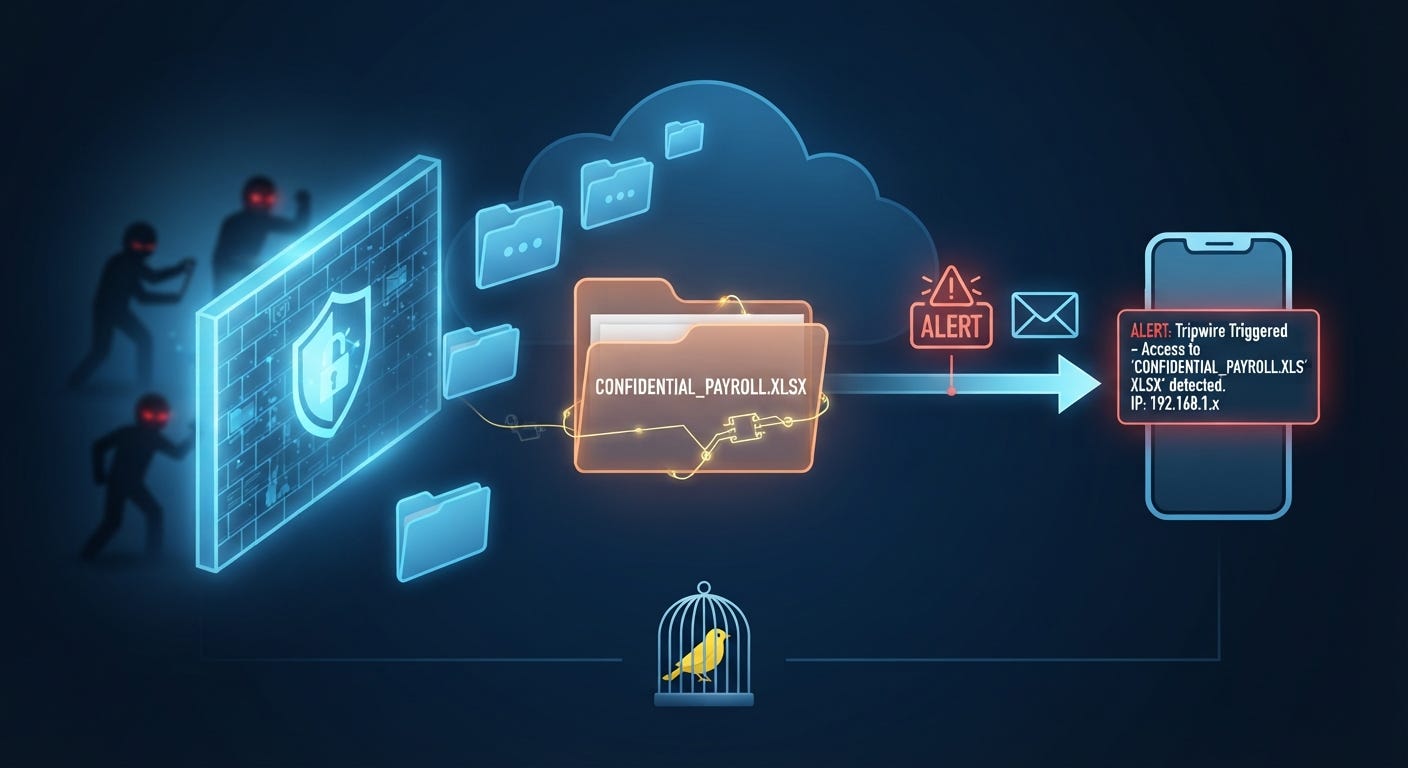
Most cybersecurity defenses are designed to keep attackers out. Firewalls block connections. Antivirus software detects malware. Password managers strengthen account security.
But what happens if someone gets past those defenses?
That is where a surprisingly simple tool called a canary token can provide an early warning that something isn’t right.
Think of a canary token as a digital tripwire. Instead of preventing an intruder from accessing your files, it alerts you when someone touches something they should never have opened in the first place.
What Is a Canary Token?
A canary token is a decoy file, link, or document designed to trigger an alert when it is accessed.
For example, you might create a fake file named:
passwords.txt
employee_salaries.xlsx
tax_return_2025.pdf
confidential_notes.docx
The file appears legitimate, but hidden inside is a tracking mechanism. If anyone opens the file, you receive an alert by email.
The concept is similar to placing a marked envelope in a desk drawer. If the envelope is disturbed, you immediately know someone has been snooping.
Why This Approach Is Different
Most security tools are reactive. They detect malware after it appears or notify you after suspicious activity has already occurred.
Canary tokens work differently.
They are designed to identify unauthorized curiosity. The moment someone opens a file that should never be touched, you know something may be wrong.
This can provide valuable early warning in situations such as:
Unauthorized access to a workstation
Insider threats
Shared computer misuse
Compromised cloud storage accounts
Curious attackers exploring your files after gaining access
In many cases, the alert arrives long before an attacker causes significant damage.
How to Set One Up
One of the easiest ways to create a canary token is through the free service available at canarytokens.org.
The process typically takes only a few minutes:
Visit the website.
Select a file based token.
Enter the email address where you want alerts delivered.
Generate the tokenized file.
Place the file in a location that should never be accessed.
Good locations include:
Archive folders
Administrative directories
Sensitive project folders
Backup locations
Personal document repositories
The key is choosing a location where no legitimate user should have a reason to open the file.
A Low-Cost Layer of Defense
Canary tokens are not a replacement for strong passwords, multifactor authentication, endpoint protection, or backups.
However, they add something many security tools lack: visibility into unexpected behavior.
For individuals, freelancers, journalists, digital nomads, and small businesses, canary tokens offer a simple way to detect suspicious activity without purchasing expensive monitoring solutions.
Sometimes the most effective security tool isn’t the one that blocks an attack. It’s the one that tells you an attack may have already begun.
Have you ever discovered someone accessing files or systems they weren’t supposed to? What early warning tool helped you catch it or what do you wish you had in place at the time?