


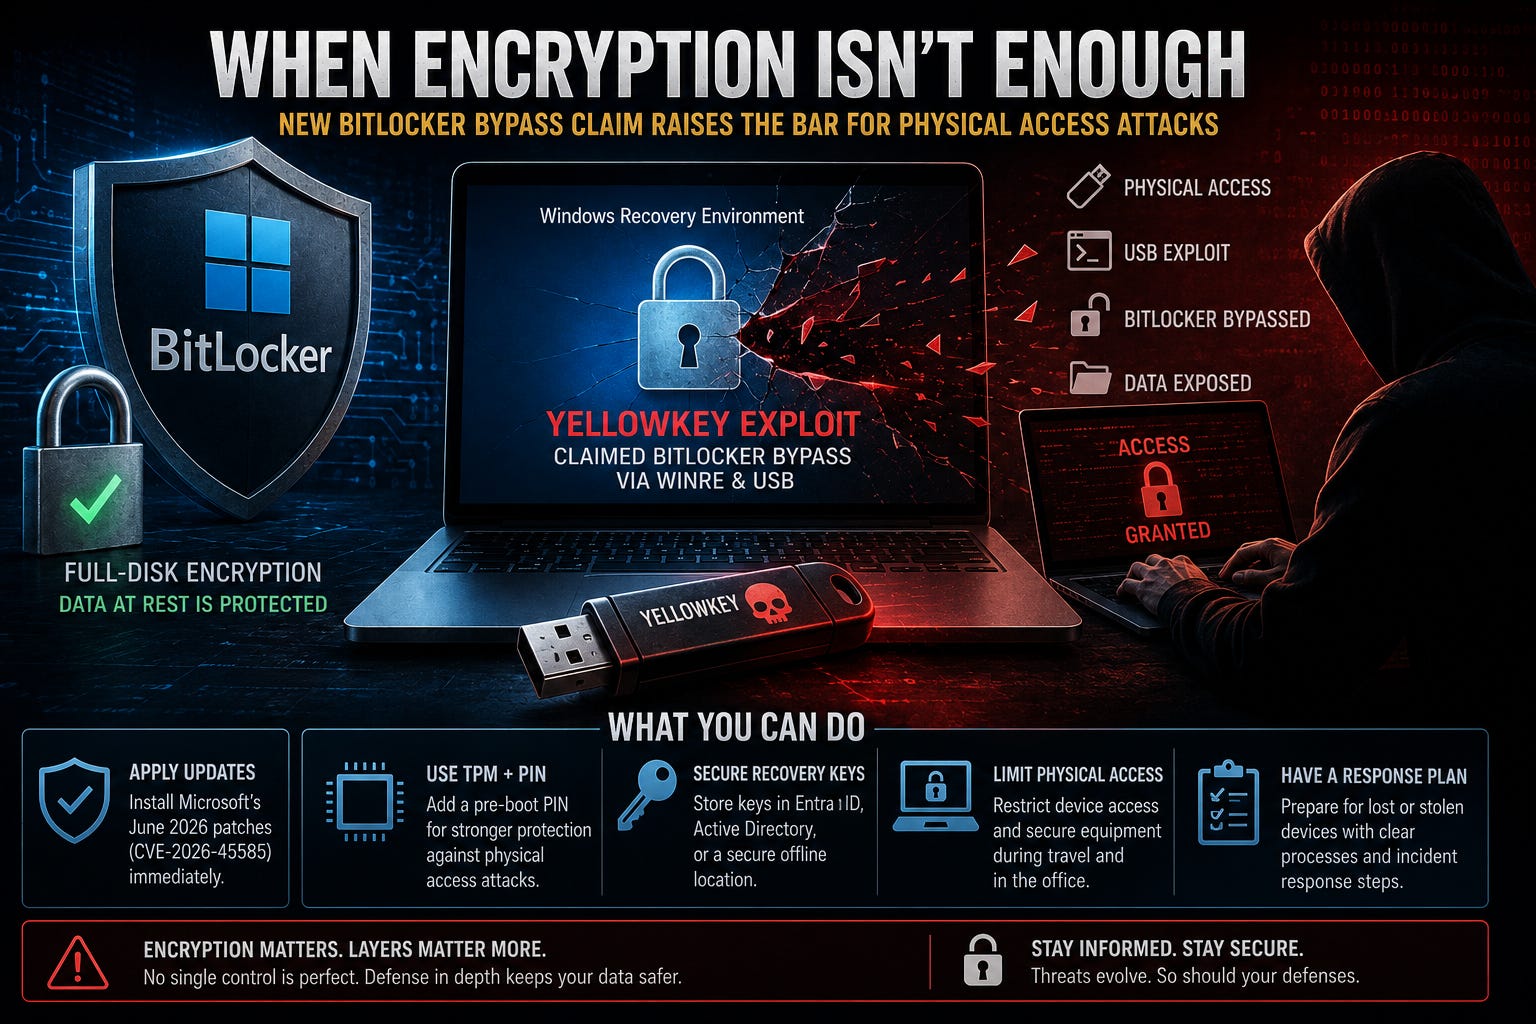
Microsoft’s BitLocker has long been considered one of the most important security features protecting Windows devices. It is designed to keep data safe even if a laptop is lost, stolen, or physically accessed by an attacker.
That trust is now being tested.
A security researcher known as Nightmare Eclipse has publicly released details of a BitLocker bypass technique called YellowKey, claiming it allows access to encrypted Windows 11 drives using a specially prepared USB device and the Windows Recovery Environment (WinRE).[1][2]
The vulnerability has already become part of a larger and increasingly public dispute between Microsoft and independent security researchers over how vulnerabilities are handled and disclosed.[3]
While Microsoft has since released patches and mitigations, the incident raises an important question:
What happens when one of the most trusted security features in Windows can be bypassed without needing the user’s recovery key?
The answer has implications for businesses, government agencies, and everyday users alike.
Why It’s Important
BitLocker is Microsoft’s full disk encryption technology.
Its primary purpose is simple:
If someone gains physical access to your computer, they should not be able to read the contents of your drive without authorization.
For organizations handling sensitive information, BitLocker serves as a critical layer of defense against:
Device theft.
Lost laptops.
Insider threats.
Unauthorized forensic access.
Data exposure after hardware disposal.[4]
The YellowKey disclosure attracted attention because it appears to challenge one of the assumptions many users have about encryption.
Many people assume that once BitLocker is enabled, their data is completely protected.
In reality, encryption is only as strong as the systems surrounding it.
Researchers claim YellowKey abuses behavior within Windows Recovery Environment and the way BitLocker interacts with Trusted Platform Module (TPM) protections under certain configurations.[2][5]
If the claims are accurate, an attacker with physical access to a device could potentially gain access to encrypted data without knowing the user’s password or recovery key.[2]
That distinction is important.
This is not a remote attack.
An attacker cannot exploit this vulnerability over the internet.
However, physical access attacks remain highly relevant for:
Traveling professionals.
Government personnel.
Journalists.
Executives.
Managed service providers.
Organizations with field deployed devices.
As recent years have shown, physical access often remains one of the fastest ways to compromise sensitive systems.
What It Is / How It Works
According to public disclosures, YellowKey targets the interaction between BitLocker and Windows Recovery Environment (WinRE).[2][5]
Researchers claim the attack can be performed using a USB device containing specially crafted files.
The exploit allegedly allows an attacker to access an elevated recovery environment that bypasses expected BitLocker protections.[2]
Reports indicate the attack primarily affects:
Windows 11.
Windows Server 2022.
Windows Server 2025.[5][6]
Windows 10 appears largely unaffected based on current reporting.[5]
The researcher behind the disclosure argued that the behavior resembles a hidden backdoor because of how reliably the bypass functions under default configurations.[2][7]
Microsoft has not characterized it as a backdoor.
Instead, the company assigned the issue CVE-2026-45585 and addressed it through its June 2026 Patch Tuesday updates.[8]
Security researchers generally describe the issue as a security feature bypass rather than evidence of intentional functionality.[8]
This distinction matters because “backdoor” implies deliberate design, while a security bypass typically results from unintended interactions between components.
At present, no public evidence has emerged demonstrating intentional functionality by Microsoft.
The Bigger Story: Encryption Is Not a Silver Bullet
One reason this story generated significant attention is because it challenges a common misconception about disk encryption.
Encryption protects data.
It does not eliminate every attack path.
Think of encryption like a vault.
A strong vault protects what’s inside.
However, if someone discovers a hidden maintenance entrance that was overlooked during construction, the vault itself may still be functioning exactly as designed.
The problem lies in the surrounding system.
Historically, researchers have demonstrated several ways physical access can weaken encryption protections:
Cold boot attacks.
TPM extraction attacks.
DMA attacks.
Firmware manipulation.
Recovery environment abuse.[9]
Academic research has repeatedly shown that TPM-backed encryption can be vulnerable when attackers gain sufficient physical access and time with a target system.[10]
The YellowKey disclosure appears to fit within that broader category.
The takeaway is not that BitLocker is broken.
The takeaway is that encryption should be viewed as one component of a layered security strategy rather than a complete solution by itself.
Want to support my work? Consider buying me a coffee. ☕
The Growing Conflict Over Vulnerability Disclosure
The technical details are only half the story.
The other half involves the increasingly public dispute between Microsoft and researchers operating under aliases such as Nightmare-Eclipse and Chaotic Eclipse.[3][11]
Over the past several months, multiple vulnerabilities including:
BlueHammer.
RedSun.
GreenPlasma.
MiniPlasma.
YellowKey.
have been publicly disclosed outside traditional coordinated disclosure processes.[3][11]
Researchers argue that vendors sometimes move too slowly.
Vendors argue that public disclosure before fixes are available puts users at unnecessary risk.
Both sides believe they are protecting users.
The challenge is that every public exploit release creates a race between defenders and attackers.
When proof-of-concept code becomes widely available, organizations must act quickly to reduce exposure.
That dynamic is becoming increasingly common throughout the cybersecurity industry.
How to Mitigate
Organizations using BitLocker should review their configurations and ensure systems are fully updated.
Install Security Updates Immediately
Microsoft addressed YellowKey through June 2026 security updates.[8]
Applying patches remains the most important defensive measure.
Consider TPM + PIN Protection
Many organizations rely on TPM-only deployments because they improve usability.
However, adding a pre-boot PIN introduces an additional authentication factor that can significantly increase resistance against physical-access attacks.[7]
Restrict Physical Access
Many advanced attacks still require direct access to a device.
Strong physical security remains an important cybersecurity control.
Monitor Device Theft Procedures
Organizations should maintain clear processes for:
Lost devices.
Stolen laptops.
Employee departures.
Hardware disposal.
Rapid response reduces potential exposure.
One practical security tool worth considering is Microsoft Intune. Device management platforms help organizations enforce encryption policies, monitor compliance, and respond quickly when devices are lost or stolen.
Disclosure: Product recommendations may include affiliate links. If you purchase through those links, I may earn a commission at no additional cost to you. Affiliate relationships do not influence my analysis, findings, or recommendations.
How to Configure/Use BitLocker More Securely
Organizations looking to strengthen BitLocker deployments should consider additional hardening measures.
Enable TPM + PIN Mode
This adds an authentication step before Windows loads.
For many high risk users, the slight inconvenience is worth the additional protection.
Secure Recovery Keys
Recovery keys should never be stored solely on the protected device.
Use:
Microsoft Entra ID.
Active Directory.
Secure password managers.
Offline secure storage.
Limit Recovery Environment Access
Review whether unrestricted access to recovery tools is necessary for all devices.
Audit Encryption Policies Regularly
Encryption settings often drift over time.
Routine reviews help identify:
Non-compliant devices.
Missing recovery keys.
Legacy configurations.
Policy exceptions.
Frameworks such as NIST and ISO 27001 emphasize layered security controls precisely because no single technology can eliminate every risk.
Feature Highlight
Closing encouragement
The YellowKey disclosure is a reminder that cybersecurity is rarely about finding a perfect defense.
It is about reducing risk through layers of protection.
BitLocker remains an important and valuable security technology.
At the same time, incidents like this highlight why organizations should avoid relying on any single control to protect sensitive information.
Encryption, physical security, patch management, identity controls, and monitoring all work together to create stronger defenses.
The organizations that adapt fastest are usually the ones that recover best when new vulnerabilities emerge.
Do disclosures like YellowKey increase your confidence in independent security research, or do they raise concerns about the growing trend of public zero-day releases?
Sources
[1] The Register, “Nightmare-Eclipse Drops Claimed BitLocker Bypass for Microsoft Windows”
https://www.theregister.com/security/2026/06/11/nightmare-eclipse-drops-claimed-bitlocker-bypass-for-microsoft-windows/
[2] Ars Technica, “Zero-Day Exploit Completely Defeats Default Windows 11 BitLocker Protections”
https://arstechnica.com/security/2026/05/zero-day-exploit-completely-defeats-default-windows-11-bitlocker-protections/
[3] Windows Central, “Microsoft Backs Off Legal Threats Against Windows Security Researchers”
https://www.windowscentral.com/microsoft/microsoft-backs-off-legal-threats-against-windows-security-researchers
[4] Microsoft BitLocker Documentation
https://learn.microsoft.com/windows/security/operating-system-security/data-protection/bitlocker/
[5] TechSpot, "A Security Researcher Says Microsoft Secretly Built a Backdoor into BitLocker, Releases an Exploit to Prove It"
https://www.techspot.com/news/112410-security-researcher-microsoft-secretly-built-backdoor-bitlocker-releases.html
[6] Windows Central, "Windows 11's June Update Shuts Down a BitLocker Flaw with Full File Access"
https://www.windowscentral.com/microsoft/windows-11s-june-update-shuts-down-an-intentional-bitlocker-backdoor-with-full-file-access-heres-what-changed
[7] Tom's Hardware, "Microsoft BitLocker-Protected Drives Can Now Be Opened with Just Some Files on a USB Stick"
https://www.tomshardware.com/tech-industry/cyber-security/microsoft-bitlocker-protected-drives-can-now-be-opened-with-just-some-files-on-a-usb-stick-yellowkey-zero-day-exploit-demonstrates-an-apparent-backdoor
[8] Microsoft June 2026 Patch Tuesday Coverage and CVE-2026-45585 Reporting
https://www.techradar.com/pro/security/microsoft-breaks-patch-tuesday-record-with-fixes-for-over-200-security-flaws
[9] CISA Guidance on Physical Access and Device Security
https://www.cisa.gov/
[10] “faulTPM: Exposing AMD fTPMs’ Deepest Secrets,” Academic Research Paper
https://arxiv.org/abs/2304.14717
[11] TechSpot, “Windows BitLocker Exploit Sparks Messy Feud Between Microsoft and the Researcher Who Exposed It”
https://www.techspot.com/news/112576-windows-bitlocker-exploit-sparks-messy-feud-between-microsoft.html